Governance Frameworks
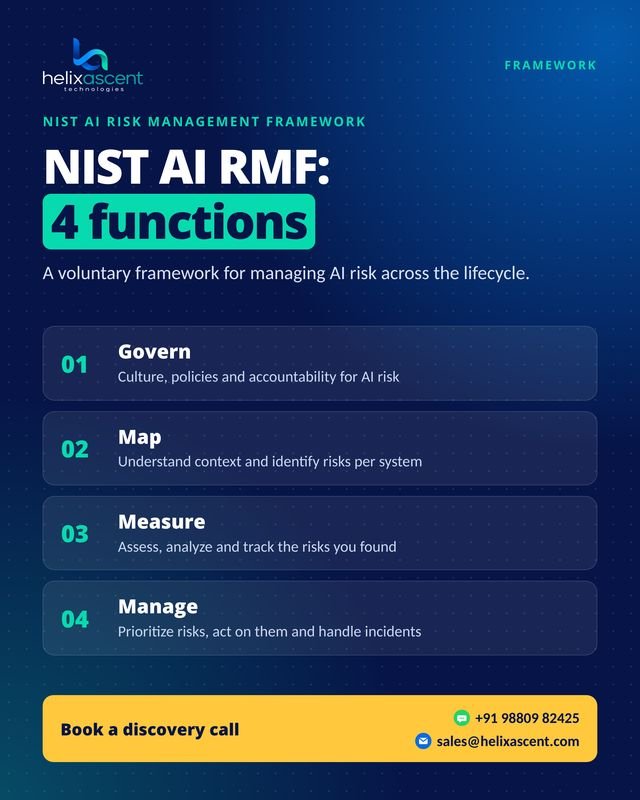
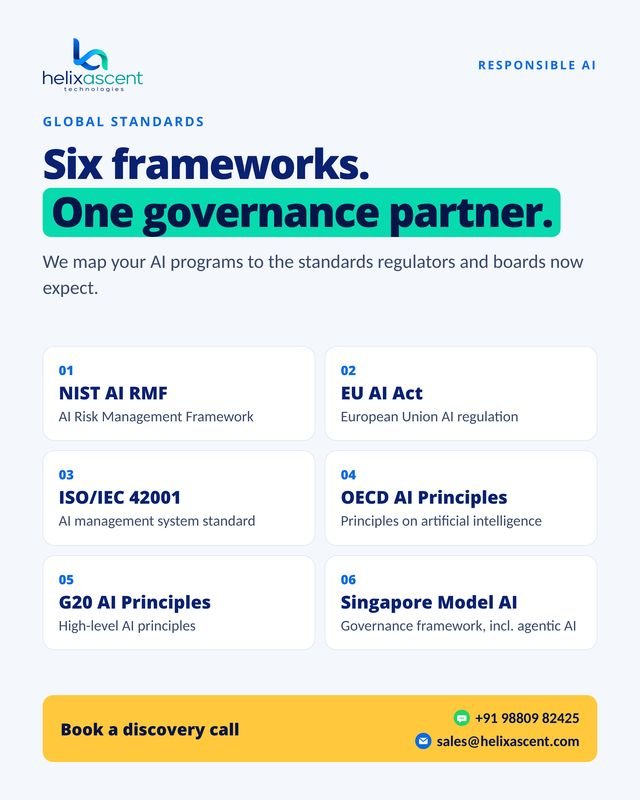
Frameworks and policies mapped to NIST AI RMF, the EU AI Act, ISO/IEC 42001, ISO/IEC 27090 and ISO/IEC 27001.
- AI governance maturity assessment
- Framework, policy and acceptable-use design
- Roles, RACI and approval workflows
Frameworks, risk controls and Responsible AI by design, mapped to the EU AI Act, NIST AI RMF, ISO/IEC 42001, ISO/IEC 27090 and ISO/IEC 27001, for generative and agentic AI.
Governance frameworks, Risk management, Compliance, AI lifecycle controls and Reusable accelerators.
Frameworks and policies mapped to NIST AI RMF, the EU AI Act, ISO/IEC 42001, ISO/IEC 27090 and ISO/IEC 27001.
Identify, assess and reduce AI risk before and after launch.
Meet regulatory and certification requirements with audit-ready evidence.
Controls from design to retirement, so every AI system stays governed.
Ready-made templates and toolkits that shorten the time to governance.
Book a discovery call and we will recommend the right starting point for your organisation.
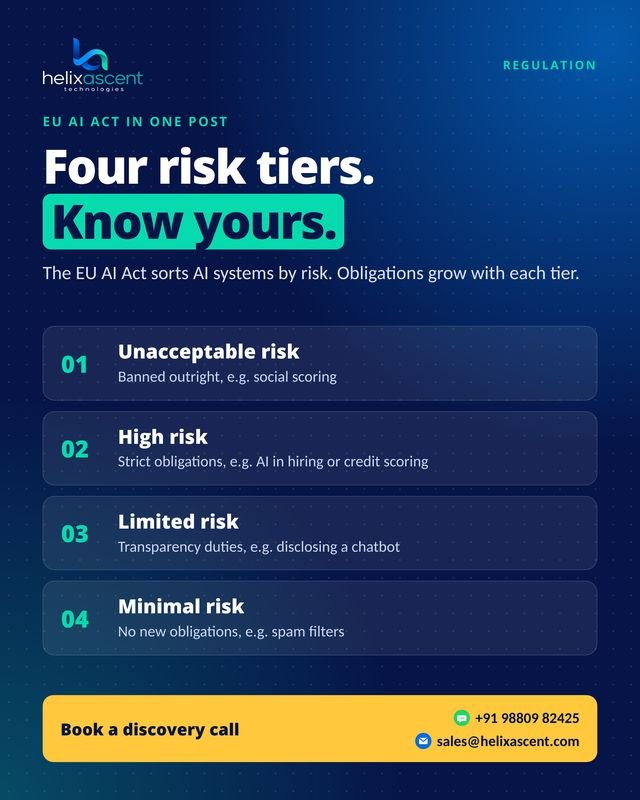
Book a discovery call| Risk tier | What it means | Example |
|---|---|---|
| Unacceptable risk | Banned outright | Social scoring |
| High risk | Strict obligations: risk management, data governance, documentation, human oversight | AI in hiring or credit scoring |
| Limited risk | Transparency duties | Disclosing that users are talking to a chatbot |
| Minimal risk | No new obligations | Spam filters |
Short explainers our team shares with leaders and risk teams every week.
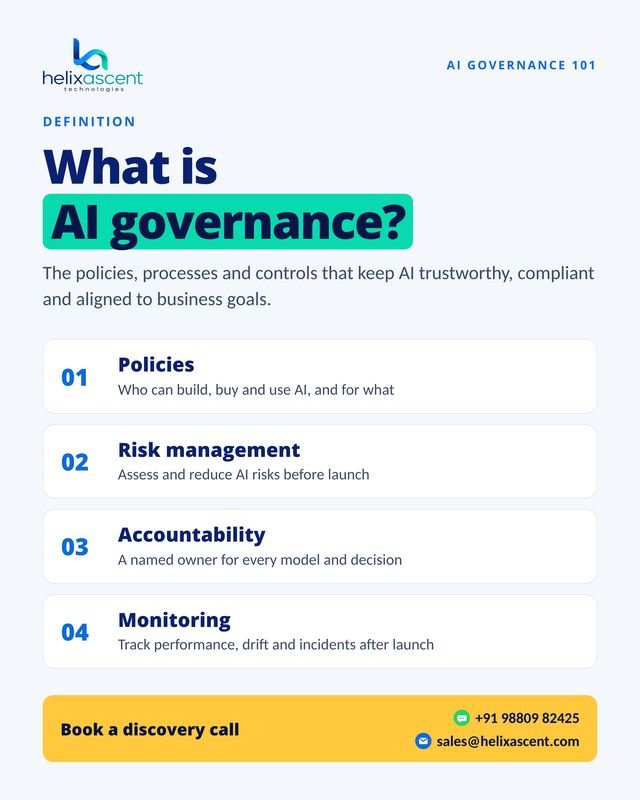
AI governance is the set of policies, processes, roles and controls that keep AI systems trustworthy, compliant and aligned with business goals across their lifecycle, from use-case approval to monitoring after launch.
It can. The EU AI Act applies to providers and deployers whose AI systems are placed on the EU market or whose outputs are used in the EU, regardless of where the company is based. We help you classify systems by risk tier and plan the obligations that apply.
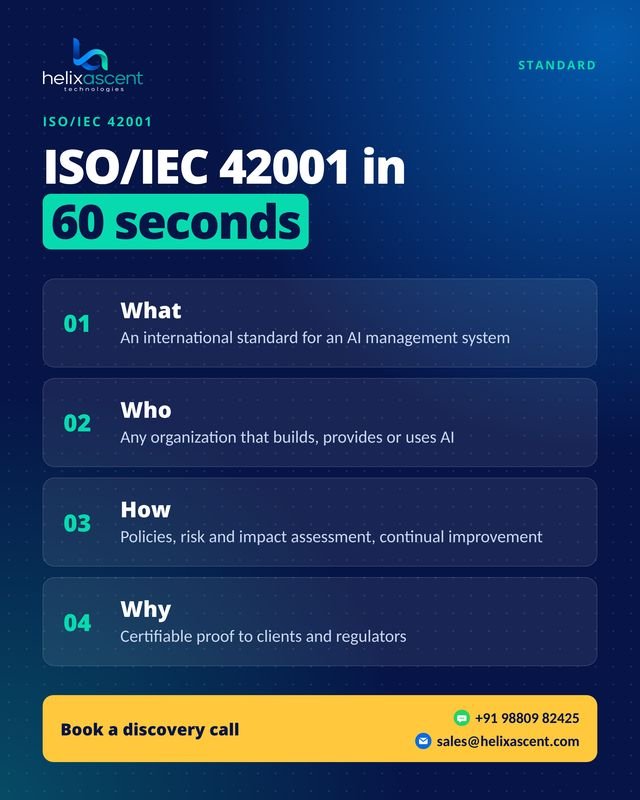
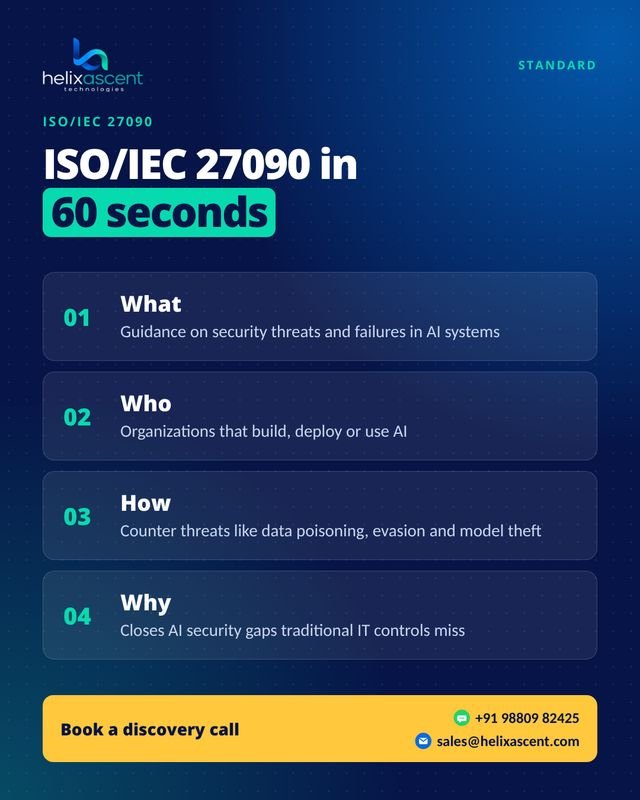
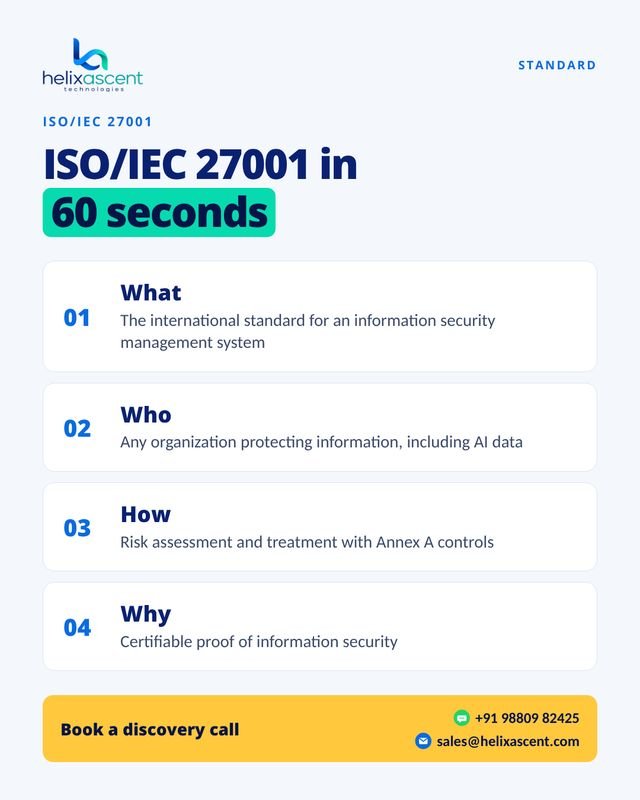
ISO/IEC 42001 is the international standard for an AI management system (AIMS). It sets requirements for AI policy, roles, risk assessment, impact assessment, controls and continual improvement, and organisations can be certified against it. We implement it together with ISO/IEC 27090 guidance on security threats to AI systems and ISO/IEC 27001 for information security.
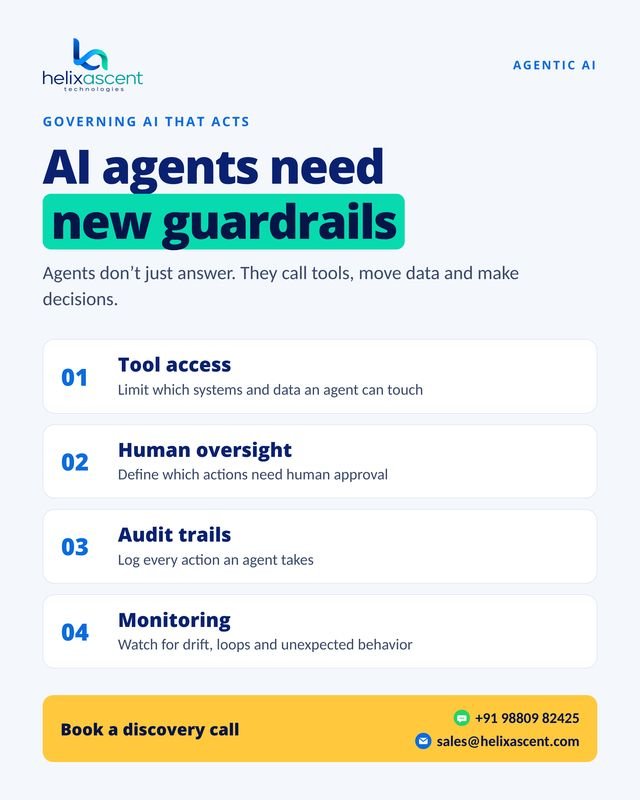
Agentic AI needs controls beyond model governance: scoped tool permissions, human approval for high-impact actions, execution limits, audit logs, evaluation before release and monitoring for loops and misuse. We design these as policy-as-code wherever possible.
A focused maturity assessment and roadmap typically takes a few weeks. Framework design and implementation run longer and depend on the number of AI systems and teams in scope. We agree the scope with you after a discovery call.
AI Strategy, Transformation, Governance, Operating Models, CoE Design.
GenAI implementation, AI agent governance monitoring, Guardrails, Policy-as-code and production enablement.
Executive education, AIGP certification with roles-based learning, Hands-on governance labs and Technology trainings for Data & AI Practitioners.
Book a discovery call. We will review where you are, what regulators will expect and the fastest path to governed, scalable AI.
 +91 98809 82425WhatsApp us